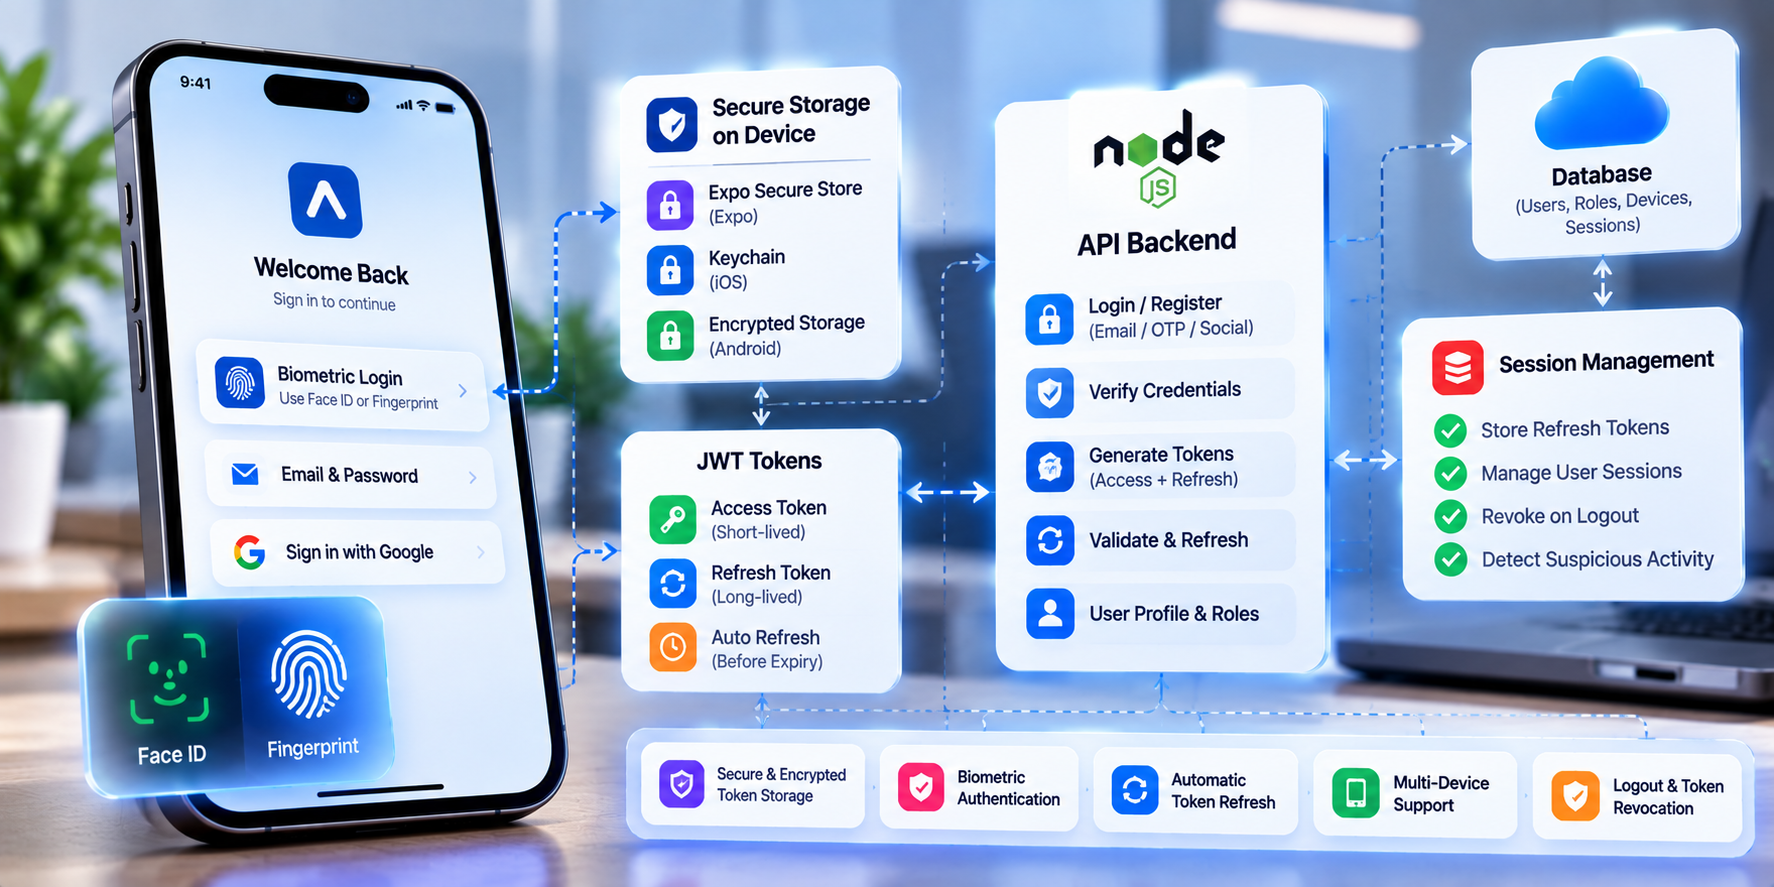
Authentication Architecture for Mobile Applications: Biometrics & Secure Storage
AsyncStorage on React Native stores data in unencrypted plaintext on disk. Authentication tokens must be saved in iOS Keychain and Android Keystore.
Why This Matters
Prevents credential extraction and token theft from rooted or jailbroken mobile devices.
Core Concepts & Architecture
Hardware-backed keystores encrypt tokens with device-specific cryptographic chips (Secure Enclave / StrongBox).
Implementation Details
Adoption of react-native-keychain, expo-secure-store, and LocalAuthentication biometrics.
Practical Code Example
The following code illustrates this pattern in a production-ready implementation:
import * as SecureStore from 'expo-secure-store';

export async function storeSessionToken(token: string) {
  await SecureStore.setItemAsync('auth_token', token, {
    keychainAccessible: SecureStore.WHEN_UNLOCKED_THIS_DEVICE_ONLY,
  });
}
Production Considerations
When deploying this in production environments:
- Enforce strict typing and runtime schema validation on all public ingestion vectors.
- Implement defensive rate limiting, connection pooling, and graceful process shutdown.
- Monitor execution latencies using structured telemetry, APM traces, and health check endpoints.
Performance, Security & Scalability
- Security & Authorization: Validate inputs, sanitize database queries, and maintain strict access boundaries.
- Scalability: Design for stateless horizontal scaling and leverage connection pooling and edge caching.
- Telemetry: Track P95 and P99 latency percentiles to detect regressions early in staging.
Common Mistakes & Best Practices
Common Mistakes
- Neglecting Edge Case Validation: Failing to handle network partitions or invalid payloads gracefully.
- Hardcoding Configuration: Always inject environment variables and avoid magic constants in domain code.
Best Practices
- Idempotency: Guarantee safe retries on state-mutating operations.
- Automated CI/CD: Run regression test suites in isolated branches before cutting over production traffic.
Conclusion
Securing refresh tokens with iOS Keychain, Android Keystore, and FaceID/Fingerprint gating.
Building a modern mobile or web product? Discuss your upcoming project with our software engineering team at DevMinds Technologies.
Sources & References
- Expo SecureStore Specification (Official Documentation)