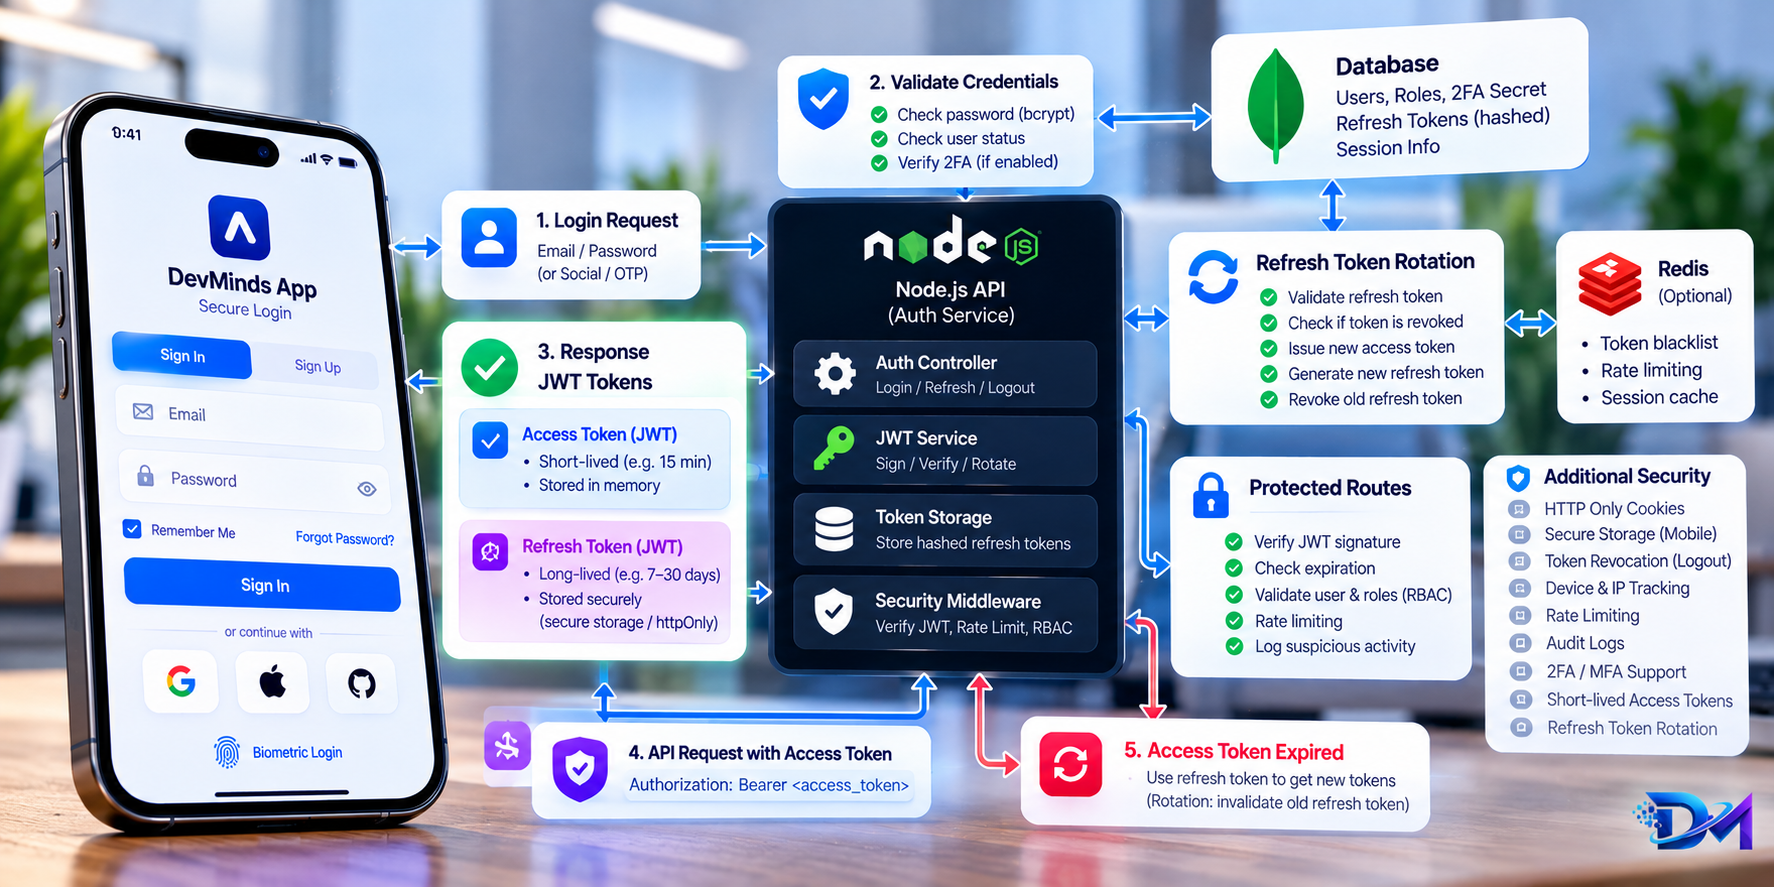
JWT Hardening & Refresh Token Rotation in Node.js Applications
Long-lived JWT access tokens cannot be revoked if stolen. Short-lived access tokens (15m) paired with single-use rotating refresh tokens mitigate risk.
Why This Matters
Protects backend sessions against token replay attacks and theft.
Core Concepts & Architecture
If a refresh token is used twice, the entire token family is revoked immediately because theft is detected.
Implementation Details
Refresh Token Family tracking in Redis/MongoDB to detect token reuse and automatically invalidate hijacked sessions.
Practical Code Example
The following code illustrates this pattern in a production-ready implementation:
// Token reuse detection: if old token is presented, revoke entire family
export async function rotateRefreshToken(token: string, familyId: string) {
  const existing = await TokenFamily.findOne({ familyId });
  if (existing && existing.revokedTokens.includes(token)) {
    await TokenFamily.deleteMany({ familyId }); // Compromise detected! Revoke all sessions!
    throw new Error('Token reuse detected! Re-authentication required.');
  }
}
Production Considerations
When deploying this in production environments:
- Enforce strict typing and runtime schema validation on all public ingestion vectors.
- Implement defensive rate limiting, connection pooling, and graceful process shutdown.
- Monitor execution latencies using structured telemetry, APM traces, and health check endpoints.
Performance, Security & Scalability
- Security & Authorization: Validate inputs, sanitize database queries, and maintain strict access boundaries.
- Scalability: Design for stateless horizontal scaling and leverage connection pooling and edge caching.
- Telemetry: Track P95 and P99 latency percentiles to detect regressions early in staging.
Common Mistakes & Best Practices
Common Mistakes
- Neglecting Edge Case Validation: Failing to handle network partitions or invalid payloads gracefully.
- Hardcoding Configuration: Always inject environment variables and avoid magic constants in domain code.
Best Practices
- Idempotency: Guarantee safe retries on state-mutating operations.
- Automated CI/CD: Run regression test suites in isolated branches before cutting over production traffic.
Conclusion
Building a bulletproof auth system: Short-lived access tokens, httpOnly cookies, and token reuse detection.
Building a modern mobile or web product? Discuss your upcoming project with our software engineering team at DevMinds Technologies.
Sources & References
- Refresh Token Rotation Security Guide (Official Documentation)